Summary
Quad Miners has presented an approach that uses context data from Network Blackbox, its Network Detection and Response (NDR) solution, as the evidence base for AI-driven threat detection and automated response. The approach connects three layers of data: original transaction and session data, behavioral baselines, and detection explainability. The company is validating it in operational environments together with existing security tools and large language models (LLMs).
Context Data as the Foundation for AI Decisions
On October 27, 2026, Quad Miners (Co-CEOs Beomjoong Park and Jaewan Hong) presented an approach to AI-based security operations. The approach prioritizes securing the context data that supports AI judgments, ahead of model performance. At its core is Network Blackbox, a context data-centric, AI-based security observability platform.
Three Layers of Context Data
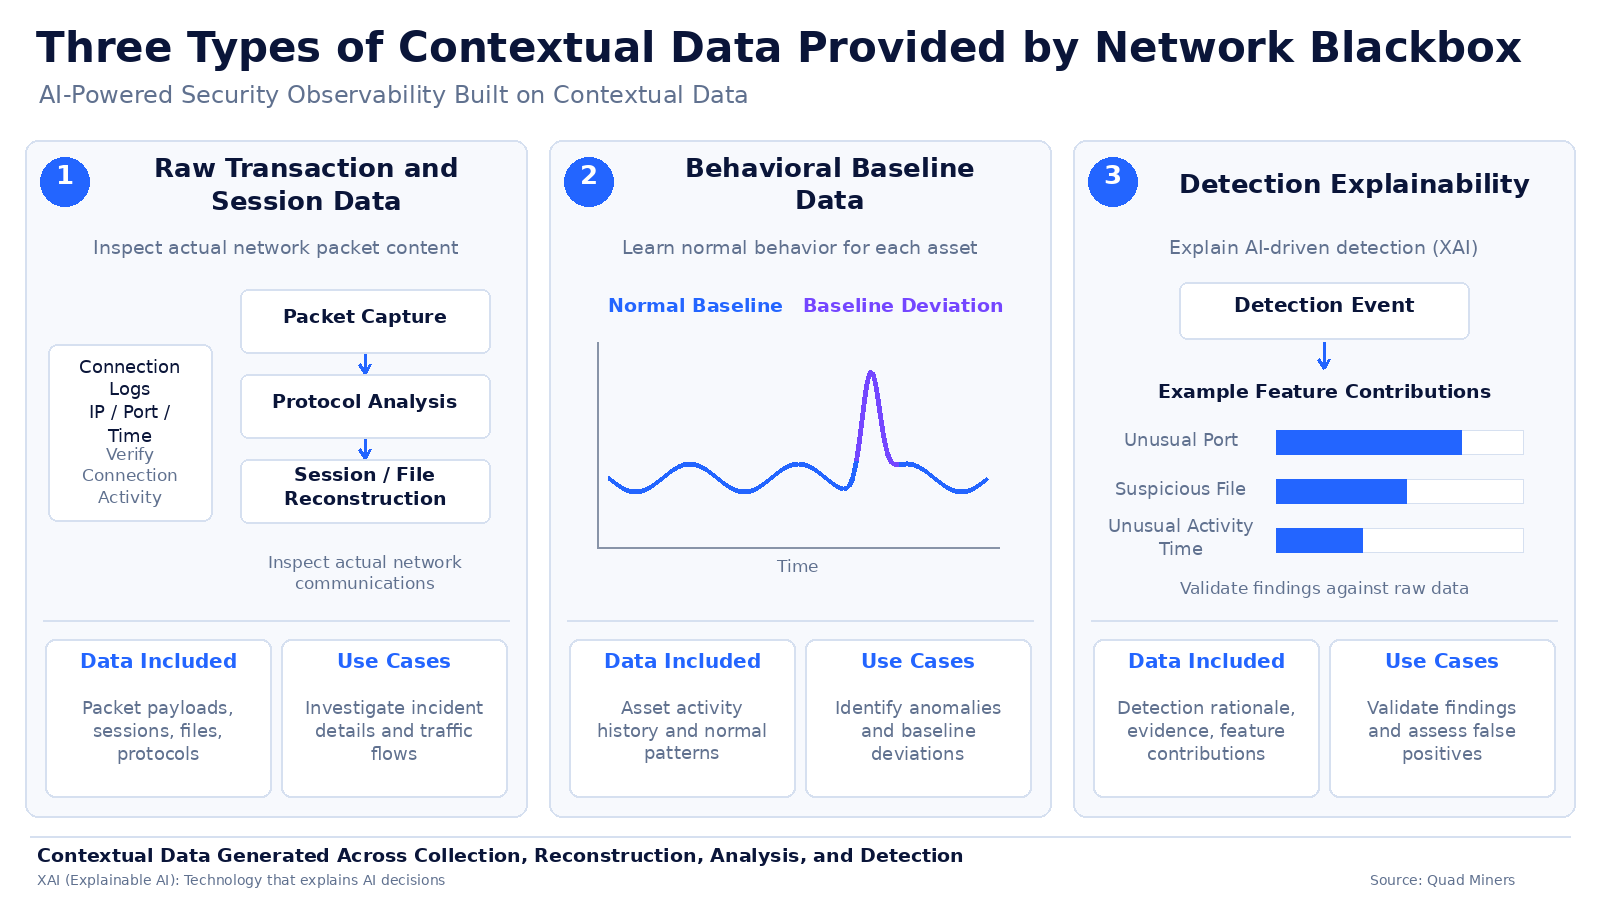
Network Blackbox generates context data through full-packet capture, session and file reconstruction, behavioral analysis, and threat detection. The data is organized into three connected layers that together show the basis for each AI judgment:
- Original Transaction and Session Data: Contains the actual content of network communications.
- Behavioral Baseline: Serves as a per-asset reference point for comparing activity.
- Detection Explainability: Shows the grounds on which a detection was made.
AI Capabilities
Quad Miners applies AI to asset behavior anomaly detection, comparing session-level activity against each asset’s baseline. Its threat hunting combines multiple indicators, such as repeated requests and parameter tampering, to trace attack scenarios. Network Blackbox also explains the basis of each detection in natural language, which helps security analysts assess whether an alert is a false positive.
Integration with Existing Security Operations
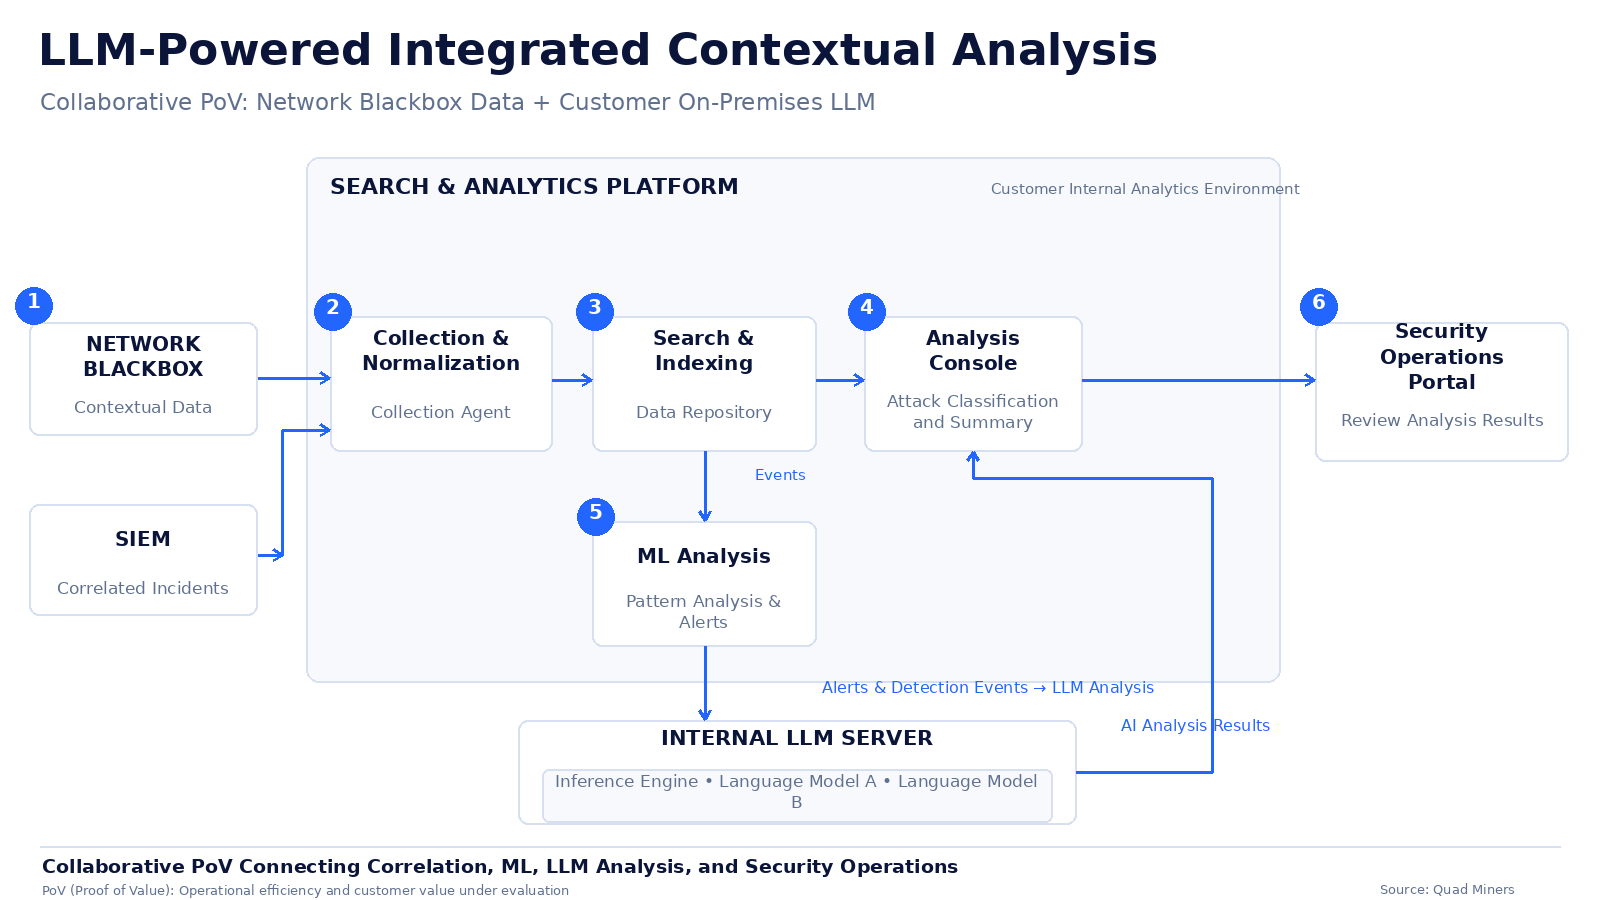
Context data from Network Blackbox connects to existing security operations tools, including SIEM, EDR, and SOAR. Detection results can then lead to concrete response actions, such as identifying suspicious endpoints and blocking traffic at the firewall.
Proof of Value in a Telecom Operator Environment
Quad Miners is running a Proof of Value (PoV) to assess the operational value of LLM-based attack scenario analysis in a telecom operator’s security monitoring environment. In this setup, context data from Network Blackbox is normalized and analyzed with machine learning, and an LLM then analyzes the attack scenarios.
Company Statement
The company stated that it will continue to support AI-based security operations through context analysis grounded in original network data.
This content was compiled based on facts confirmed in an article published by Electronic Times (etnews) on October 27, 2026 (bylined by reporter Park Jong-jin).