Summary
SecuLayer and Quad Miners have signed a strategic memorandum of understanding (MOU) to jointly pursue cybersecurity solution business and enter overseas markets together. The two companies will integrate SecuLayer’s AI-based SIEM·SOAR platform, eyeCloudXOAR, with Quad Miners’ NDR solution, Network Blackbox, to deliver context-based security observability and a next-generation SOC solution. They plan to secure joint references within the third quarter and expand into the public, financial and global markets, building on their joint work on a SOC project in Indonesia.
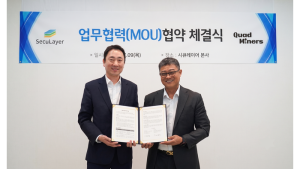
SecuLayer (CEO Juho Jeon), a Korean company specializing in AI-based information security solutions, and Quad Miners (CEO Beomjung Park), a company specializing in cybersecurity observability and network detection and response (NDR), have signed a strategic MOU to jointly pursue cybersecurity solution business and enter overseas markets together.
As AI-driven cyberattacks become more sophisticated and automated, the need for an end-to-end defense system that handles everything from threat detection to root-cause analysis and automated response has grown. However, fragmented log or network data alone has made it difficult to fully understand the context and flow of an attack, limiting precise analysis and rapid response. Overcoming this requires an approach based on context data, which interprets the relationships between events and the flow of behavior as a whole.
Integrating SIEM·SOAR and NDR Through Context Data
To address these limitations, the two companies will integrate SecuLayer’s AI-based integrated security platform (SIEM·SOAR), eyeCloudXOAR, with Quad Miners’ NDR solution, Network Blackbox, which applies context-data-centric AI-based security observability technology.
The integration will reconstruct diverse security events, including logs and network traffic, into context data and use it to precisely analyze the causal relationships and attack flows behind threats. This will enable context-based security observability that goes beyond conventional visibility, and the companies plan to bring a more advanced next-generation security operations center (SOC) solution to market on this basis.
The two companies have already worked together in the global market. Their solutions’ technical integration and business viability were demonstrated during the process of winning a SOC service contract with DigiServe (PT Digital Aplikasi Solusi), an Indonesian telecom-based IT services company. The MOU formalizes this model and is expected to serve as a foundation for jointly entering the Asian and global security monitoring markets, with Indonesia as a bridgehead.
Cooperation in Five Areas, Joint References Within Q3
Under the agreement, the companies will cooperate closely in five areas: linking SIEM·SOAR with NDR and network forensics technologies to build an integrated platform; joint research on AI-based threat detection and analysis; planning, developing and commercializing a hybrid security analysis model based on context data; jointly identifying domestic and overseas markets, including the public, financial, telecom, manufacturing and defense sectors, and conducting joint sales and proposals; and joint marketing, seminars, proofs of concept (PoC) and references.
To put the agreement into practice, the two companies formed a working-level council immediately after signing. They have begun technical validation of the integrated solution and plan to secure joint references within the third quarter through joint seminars and pilot projects, then complete full-scale productization and commercialization in the second half of the year.
“Capturing Advanced Persistent Threats That Single Solutions Miss”
“Interpreting log-based status information and network-traffic-based behavioral information together as context data is essential to completing the response to AI-driven threats,” said Junbae Seo, CEO of Utron, an official partner for both companies’ products. “We will maximize the technical synergy based on our experience in supply and delivery in the field.”
“Combining the big data log analysis technology SecuLayer has built over about 15 years with Quad Miners’ cybersecurity observability and NDR technology will give us a strong competitive edge in the global market, where demand for next-generation SOC enhancement is rising rapidly,” said Juho Jeon, CEO of SecuLayer. “This cooperation will be a starting point for setting a new standard for Korea’s security industry.”
“Combining context-data-centric AI-based security observability with SIEM·SOAR goes beyond fragmented event analysis, making it possible to understand the full attack flow and intent behind a threat and to effectively capture advanced persistent threats (APTs) that were difficult to detect with a single solution,” said Beomjung Park, CEO of Quad Miners. “Building on the success proven in the DigiServe project in Indonesia, we will actively expand our cooperation to the global market, including Asia, as well as Korea.”
Since launching its big-data-based SIEM in 2012, SecuLayer has built numerous references in the public, financial and defense sectors, including the National Information Resources Service. Quad Miners supplies solutions to a range of sectors, including finance, telecommunications and the public sector, based on its context-data-centric AI-based security observability and NDR technologies.
This content was reconstructed from facts objectively verified in an article published by Electronic Times (etnews) on July 22, 2026, under the byline of reporter Lee Won-ji.